
Protect your identity and your data
Your accounts, devices and personal information are all targets for cybercriminals. A few simple habits will keep you and the Concordia community safe.
Protect yourself
Secure your accounts and learn to recognize threats in email and on the web.
Why do you need a secure password?
Because as a Concordia student, faculty, or staff, you have accounts on several university systems. Even though these accounts are password-protected, choosing a secure password is the first step to protecting yourself and your information against any kind of security threat.
For example, the netname password has the following criteria:
· Your password must be 12-16 characters in length
· Your password must include at least one lower case letter, one upper case letter, one special character (e.g. !, @, # or %) and one number.
The following are additional password tips for keeping your information safe:
- Change your password every three to six months and avoid using repeat passwords. If you wish to change your netname password now, visit the Password reset page now.
- Avoid using dictionary words, names of people, names of places, phone numbers, and birthdates. Information hackers have created software to guess passwords and these are the most commonly guessed. Your username, the word 'Password', or 123456 are also easy targets.
- Always keep your password a secret. Don't share it, and don't write it down where it may be found.
- If your web browser or an application prompts you to save your password, select ‘no’. Anyone with access to your computer could very easily log into an account as you.
- Use a password manager to create and store a different, strong password for each of your accounts. Reputable options include 1Password, Bitwarden, KeePass and Proton Pass. Protect it with a long master password and turn on MFA for the manager itself.
- Use a password for your Concordia accounts that is different from your other accounts (i.e. online banking and social media). It is best to choose a different password for each account.
- Choose a phrase for creating a password that is easy to remember and has special meaning for you.
Multi-factor authentication (MFA) adds a second step when you sign in. You approve each sign-in using the Microsoft Authenticator app. Even if someone steals your password, they can’t access your account without this second step.
What can I do to stay safe?
- Use the Microsoft Authenticator app to approve your sign-ins.
- Never approve a sign-in request you didn’t start. If you get one, deny it, change your netname password right away and report it to the Service Desk.
- Never share an MFA code, even with someone who says they’re from IT support.
- Turn on MFA for your personal accounts too, such as email, banking and social media.
What are phishing emails?
Phishing emails seek to trick users into providing confidential information such as personal data or financial information. Some try to get you to take the bait by offering deals or rewards or pretending to be a trusted source like a bank, Concordia, an employer or well-known business. They may seek to lure you on to a fraudulent site or to click links or attachments. Phishing can also arrive by text message, phone call, Teams, social media or a QR code.
What can I do about them?
- Hover over a sender’s email address with a cursor. It can reveal inconsistencies with the name of the sender.
- Think twice about opening emails with a generic greeting, rather than your name.
- Only open emails from trusted senders.
- Be suspicious of messages that create urgency or make threats, such as “Your account will be closed today” or “Act now to avoid penalties.” Phishers want you to react before you think.
- Don’t click on links or attachments unless you’re expecting them.
- If you get an unexpected call asking for money or passwords, even from someone who sounds like a person you know, hang up and call them back on a number you already have. Criminals can use AI to copy a person's voice.
- Never copy and paste a command into your computer because a website or message tells you to 'fix' a problem or 'prove you're human.
- If you’re contacted by a company with which you don’t do business, consider that the email may be phishing or spam.
- Watch for mistakes in titles or content. Spelling or grammar mistakes can be a warning sign, but many phishing messages now have none because attackers use AI to write them.
- Use Outlook's 'Report Phishing' button, or report suspicious emails to help@concordia.ca, then delete them.
What are viruses?
Viruses or malware are files or bits of code that can have a detrimental effect on your computer. They are often sent via email as an attachment with file types such as .exe, .zip and others.
What can I do about it?
Never open any attachments from unknown sources or even from trusted sources with unknown file extensions. Delete suspicious emails and do not open the attachments.
If you have opened any attachments from this type of email, change your netname password, manually prompt SentinelOne to scan your computer, and contact the Service Desk at 514-848-2424 ext. 7613 or via webform.
What is spam?
Spam is any unsolicited commercial email. Spammers send out these messages to get you to see their advertising and promote their business or product. They send the messages to thousands of people, slowing down the network and causing headaches for the user. Concordia's email filters can catch and block the majority of spam, but unfortunately, it is not possible to block all spam without also blocking some legitimate emails.
What can I do about it?
Delete or filter unsolicited email, bulk email, or unwanted email without opening or replying to it. Never provide your email address to the sites from which you do not wish to receive mail and never post your email address on public forums.
Every email that you send or receive contains two main parts: the body of the message and the header. The email header (or internet header) is a detailed log showing the path the email took from the sender to the receiver as well as the date, time, and email addresses. For instructions on how to view a message header, visit Retrieving email headers page.
Wi-Fi is inherently susceptible to security risks. Be cautious when connecting to public Wi-Fi or open hotspots.
Make sure that the site to which you are connected is encrypted before you send any personal information or sensitive information when using a hotspot. Websites use TLS technology to encrypt the information. A good way to know if this is being used is to look at the url of the webpage you are visiting. Verify that the url has https:// to make sure the connection is secure. Keep in mind that https only means the connection is encrypted, not that the site is genuine. Phishing sites use https too, so also check that the web address is exactly the one you expect.
- Ask for a connection name and other details when connecting to an open Wi-Fi network.
- Consider turning off your wireless connection when it is not being used.
- Don't allow your device to connect to wireless networks automatically.
- Use VPN connection or enable mobile data connection to access a website that may need you to provide sensitive or personal information.
Concordia has purchased SentinelOne Anti-Virus, which is proven to deliver superior and proactive protection to safeguard our university's IT environments. Learn more about SentinelOne.
What is SentinelOne?
SentinelOne Anti-Virus is a program that runs in the background of the operating system to protect your computer from malicious software and viruses. There are many ways SentinelOne helps protect your computer:
- Whether you're using your computer to browse the Internet, edit documents, or send email, SentinelOne will automatically scan all files for viruses before any actions are taken. For example, if you attempt to open a document that contains malicious software, SentinelOne will prevent it from opening and warn you of the possible threat.
- It runs numerous scans for viruses and malicious software throughout the week.
- It's controlled and monitored centrally by IITS. As a result, clients receive proper monitoring and their virus definitions remain up-to-date at all times. If any problems occur, they are easy to diagnose and resolved in a timely manner.
How do I install SentinelOne?
Learn how active faculty and staff can get SentinelOne.
Please note: Computers acquired through the Concordia standard computer purchase program will have SentinelOne installed on them at the time of initial setup by Concordia technicians.
Tips on the SentinelOne Anti-Virus interface:
- Once SentinelOne has been installed on your computer, you will notice a blue shield in the toolbar.
- Right click on the blue shield and select Open SentinelOne Anti-Virus if you wish to view the main control panel.
- When SentinelOne is not working correctly, the blue shield will turn grey and will display a red X.
- Scans will take place automatically, but users may also manually start a scan from within the control panel.
What is a keylogger?
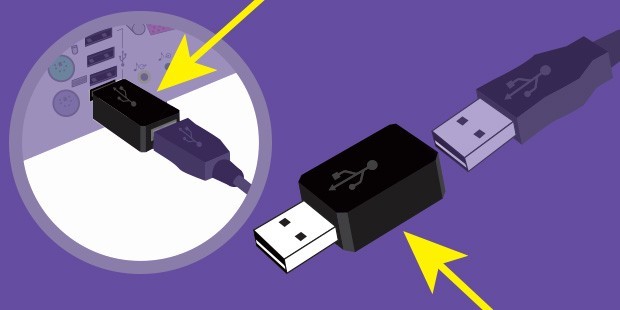
A keylogger is a device or program that records every key you press on your keyboard. Once installed, a keylogger can capture usernames, passwords, banking information, and anything else you type. Keyloggers can be a piece of physical hardware or they can also be malicious software, often hidden in email attachments or unofficial downloads. Only open files and install software from sources you trust.
A physical keylogger can vary in appearance, but will usually look like a small device connecting your computer’s keyboard cable to the computer.
What can I do about it?
Always do a visual check before using any public computer to ensure a keylogger has not been installed.
What should I do if I find a keylogger?
If you notice something suspicious on a Concordia computer, call Concordia's campus security immediately at 514-848-3717 and wait for the security officer to arrive. Do not move the computer or touch the keylogger, as fingerprints may be collected as part of the investigation.
It is important to also report the incident to Concordia's IT security department using the IT Security Incident Reporting Form.
Make a habit of logging off when you are finished using the computer or a certain website. Never leave programs or websites open for others to access. Lock your screen with a screensaver that requires a password on wakeup or turn off your system at the end of the day.
Unwanted software and free downloads can be harmful to your system. Think carefully before you download or install an unknown software on your computer. It is suggested that you only download software from reputable or trusted websites.
An unpatched device is more likely to be vulnerable and can be exploited or compromised. Therefore, keep your operating system and other software up to date by installing updates and patches regularly as they become available (this also applies to applications on your mobile device). It is recommended that you set up your device for automatic software and operating system updates.
Never leave your laptop or mobile device unattended. Always lock or secure your device when you are away from it – use a safety cable.
Set a password or code to access the mobile device and enable idle timeout to lock the mobile device's screen when it is not in use. This setting will prevent unauthorized access to the device.
A hardware failure can happen without warning and may result in the loss of important data.
Back up your data regularly on an external device – USB key or external disk – and keep a copy in a safe place.
Sensitive data should be encrypted to maximum protection.
Delete suspicious emails and do not open their attachments or click on any links. If you wish to report the suspicious email, communicate directly with the Service Desk via webform.
If you have opened any attachments from suspicious email, change your netname password, manually prompt SentinelOne to scan your computer, and contact the Service Desk at 514-848-2424 ext. 7613 or via webform.
Change your netname password right away on the Password reset page, then contact the Service Desk at 514-848-2424 ext. 7613 or help@concordia.ca.
Manually prompt SentinelOne to scan your computer and contact the Service Desk at 514-848-2424 ext. 7613 or via webform.
Please visit SentinelOne Page for more details on how Concordia computers are protected by SentinelOne.
For personal computers, Windows includes Microsoft Defender Antivirus and macOS has built-in malware protection. Keep them turned on and keep your system up to date, or install another reputable antivirus product from the vendor's official website.